Dive Brief:
- Hundreds of European supermarkets were forced to throw away tens of millions of dollars worth of grocery products Monday when hackers accessed a network-vulnerable control system and locked refrigeration units into defrost mode for several hours, according to news reports.
- Danish control system manufacturer Danfoss, which acknowledged the breach of its systems late Monday, said its AK-SM800 and AK-SC355 refrigerator regulator systems were involved in the incident. In a statement to Agence France-Presse, Danfoss called most of the affected equipment “legacy” products that "no longer receive software or security updates," AFP reported.
- Danfoss, a major supplier of building control systems in the United States, told AFP that it has long advised supermarkets to update the firmware of these models and to “migrate legacy systems to current-generation solutions."
Dive Insight:
By locking the defrost setting on, the hackers raised the temperature of the refrigeration units to up to 122 degrees Fahrenheit overnight, Reuters reported.
Units in France, Spain, Portugal, Poland, Germany and Belgium were affected, Reuters reported based on an analysis by Sekoia Threat Detection and Research, a private cybersecurity company.
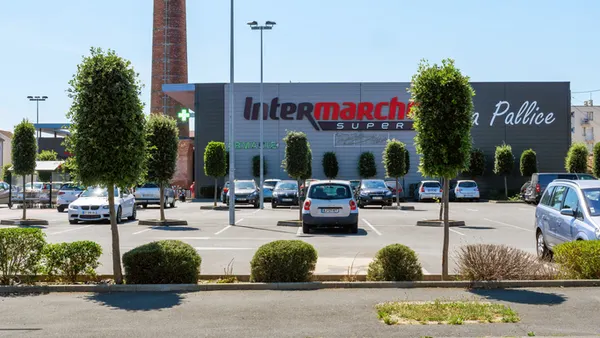
An estimated 150 refrigeration units operated by Intermarché, a France-based grocery store chain, were affected. Units in stores owned by Carrefour, Coopérative U and E Leclerc, among other European grocery stores, were also affected, according to reports.
"Targeting equipment essential to the preservation of fresh products and to the food supply of the French people is of extreme gravity and is unprecedented," Coopérative U CEO Dominique Schelcher said in a statement Monday posted on X.
Cybersecurity specialists have been raising concerns over network-connected building system vulnerabilities for years, in part because of their reliance on protocols that were designed decades ago without security in mind. In Europe, Modbus is a widely used communication protocol for building automation systems, according to a report by Armis from ServiceNow. The DanfossAK-SM800 and AK-SC355 refrigerator regulator systems are on Modbus, according to Danfoss documentation on its website. The company didn’t immediately respond to a request for comment.
The incident shows what that vulnerability can look like when the systems are exploited, Amir Preminger, chief technology officer at cybersecurity company Claroty, said in an email.
“The cyber attack … should raise the alarm for any company that is responsible for handling temperature-sensitive products,” he wrote. “Industrial control systems such as refrigeration controllers are often assumed to be on safely isolated networks [but] many of these devices are directly exposed to the public internet.”
Cybersecurity specialists previously flagged the Danfoss vulnerabilities. The U.S. Cybersecurity and Infrastructure Security Agency published an advisory on an authentication flaw in Danfoss’s AK-SM 800A system managers. And Claroty’s Team82 unit called out that system’s vulnerabilities in August.
“Our research uncovered a hidden ‘code-of-the-day’ authentication mechanism that could be abused to bypass normal authentication,” the Claroty analysis said. Other vulnerabilities were found as well.
Claroty said it informed Danfoss of the problems and that Danfoss responded by saying it had addressed them in a new firmware version.
In a report released earlier this month, Armis from ServiceNow said 73% of organizations have at least one known exploited vulnerability in their building systems. That exposure is likely to grow, it said, because 91% of the systems that organizations are using communicate over insecure protocols.
The high proportion of vulnerable systems stems in part from the legacy BACnet standard that most building systems in the U.S. use, the company says. The standard was introduced in the 1990s without security protocols because the systems at the time weren’t network-connected. The widely used Modbus standard in Europe has the same legacy vulnerabilities, according to the Armis from ServiceNow report.
“Modbus and similar standards were built for reliability in isolated networks, often without authentication or encryption,” the report says.
Having network-connected systems makes maintenance easier and reduces costs because it enables engineers to troubleshoot issues remotely, Preminger said. But “it also lowers the barrier to entry for attackers.”