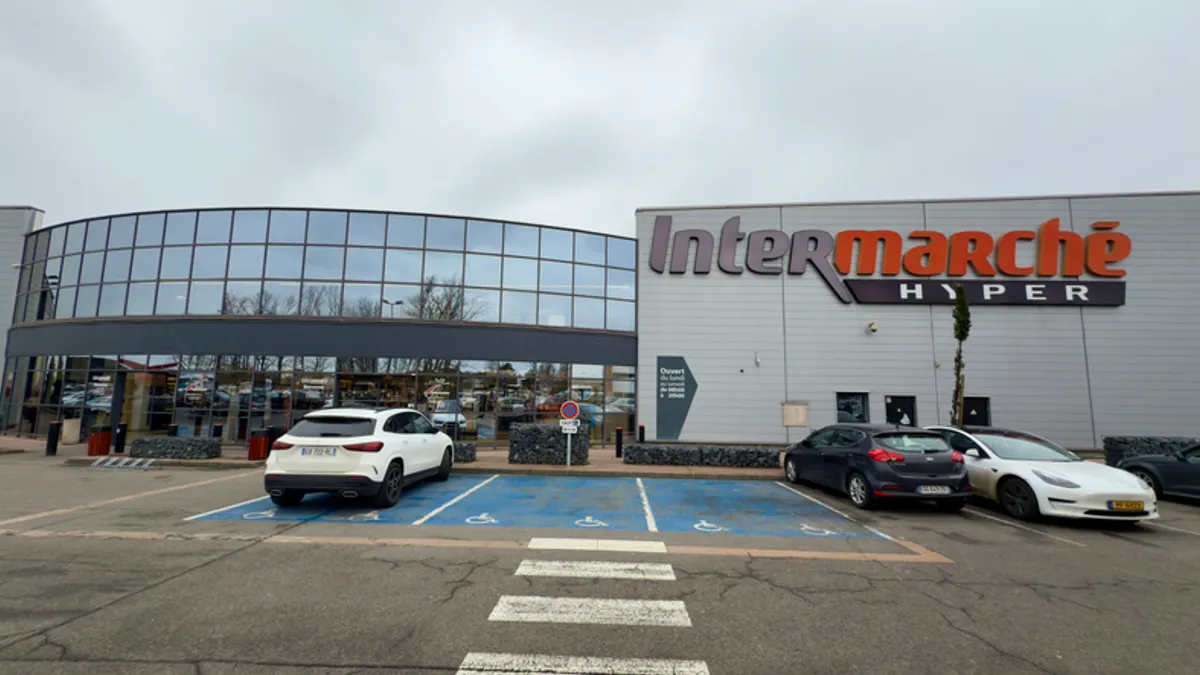
When hackers used online control systems to defrost grocery store refrigerators across Europe last week, causing tens of millions of dollars in lost food products, it showed the risk that connected building automation systems can pose.
“We’re sitting on a time bomb,” Sean Tufts, field chief technology officer at cybersecurity company Claroty, told Facilities Dive.
Security specialists have been warning about the vulnerability of building systems for years. Systems built decades ago still use communications protocols that weren’t designed with security in mind. Now that hackers have a high-profile example of how these systems can be exploited, more incidents could follow if these systems aren’t upgraded or replaced.
“For a long time, we’ve been talking about set-point tampering,” said Tufts, referring to networked temperature controls on refrigeration systems. The hackers “did that in this attack…. That’s [what] we’ve been most worried about, and now it happened [to] our food systems.”
For facilities managers, the risk shines a spotlight on the need to work with colleagues in IT and other specialty areas to put protective measures in place. Facilities Dive has compiled its most recent stories on the cybersecurity issues of building systems and what facilities managers might do to address their organization’s exposures.
Read Facilities Dive’s recent coverage of this and other cybersecurity concerns in building controls: